How to Prevent SQL Injection: 10 Security Practices Every Developer Should Follow
By Dr. Isabella Gunn · October 27, 2026
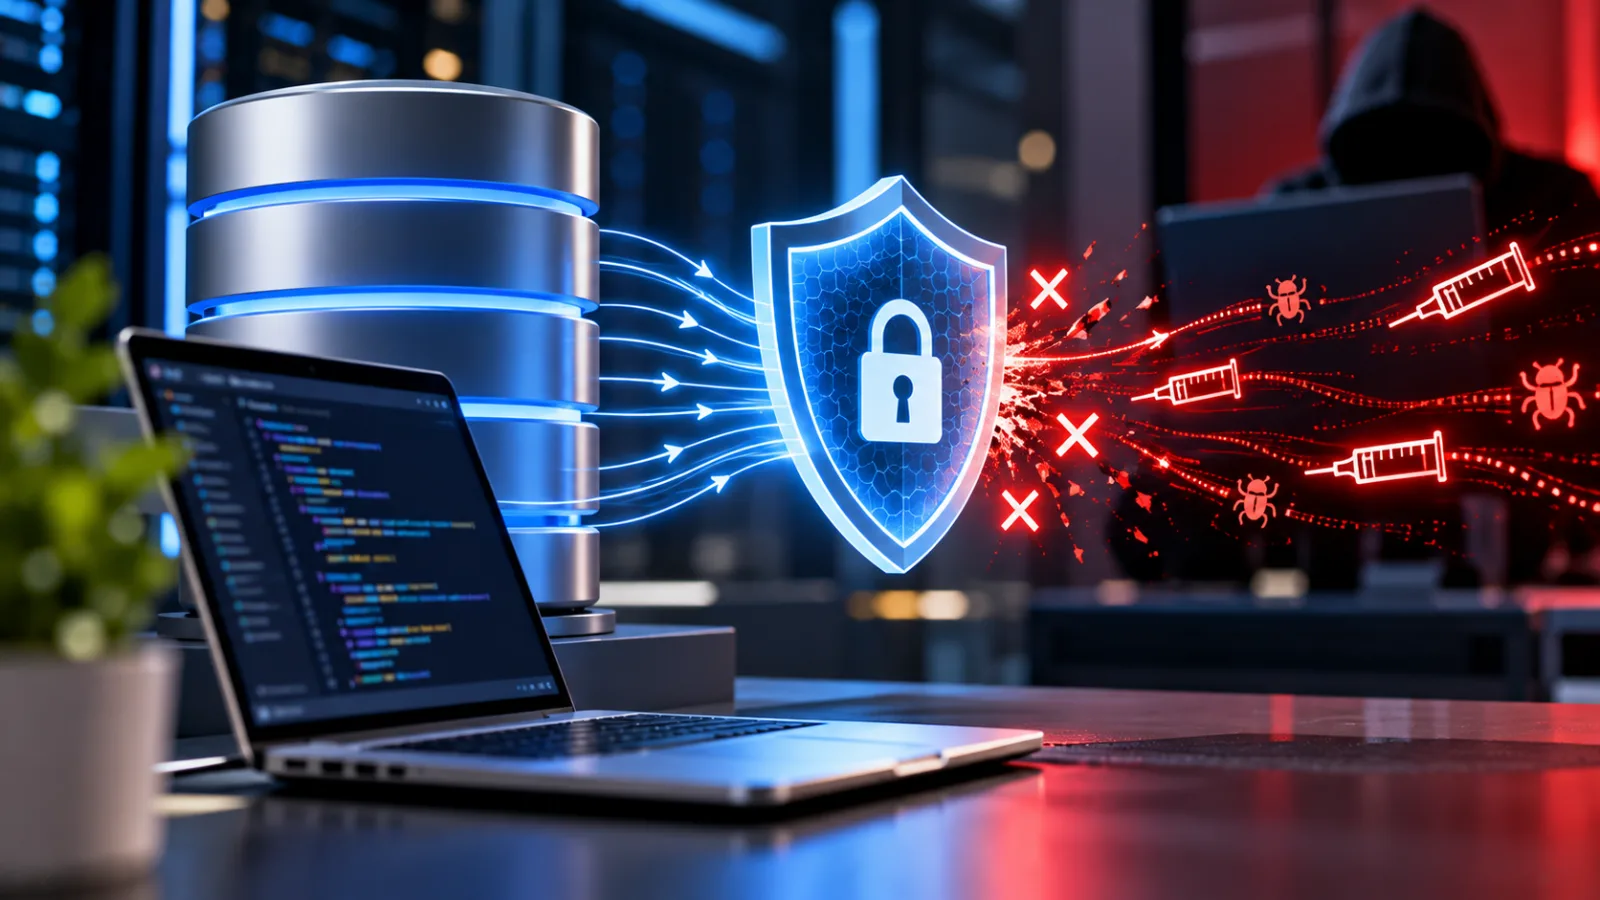
Table of contents
- What Is SQL Injection?
- Why Is SQL Injection Dangerous?
- 1. Use Parameterized Queries and Prepared Statements
- 2. Avoid Building SQL Queries Through String Concatenation
- 3. Validate Input Using Explicit Rules
- 4. Use Object-Relational Mapping Tools Correctly
- 5. Implement Stored Procedures Safely
- 6. Apply the Principle of Least Privilege to Database Accounts
- 7. Handle Database Errors Without Exposing Sensitive Information
- 8. Keep Database Software, Drivers, and Frameworks Updated
- 9. Test Applications for SQL Injection Vulnerabilities
- 10. Use a Web Application Firewall as an Additional Layer
- A Practical SQL Injection Prevention Checklist
- Final Verdict: Prevent SQL Injection at the Query Level
SQL injection is best prevented by using parameterized queries, avoiding unsafe SQL string concatenation, restricting database permissions, and testing how applications handle untrusted input.
Developers should also review stored procedures and ORM queries, validate input according to business rules, and prevent database errors from exposing sensitive information.
No single security control replaces a secure development process, but correctly implemented parameter binding is the primary defense against SQL injection in database queries.
SQL injection occurs when an application allows untrusted input to alter the structure of a database query.
Depending on the vulnerability and the database account's permissions, an attacker may be able to bypass application logic, access unauthorized records, modify information, or delete data.
The consequences can extend to customer privacy, business operations, regulatory obligations, and incident response costs.
The central security principle is straightforward: treat user input as data, never as executable SQL instructions. The Open Worldwide Application Security Project (OWASP) recommends prepared statements with parameterized queries as the primary defense, supported by appropriate input validation and least-privilege database access.
What Is SQL Injection?
SQL injection, commonly abbreviated as SQLi, is a security vulnerability that occurs when an application builds a SQL statement in a way that allows untrusted input to change the query's intended meaning.
SQL, or Structured Query Language, is used to retrieve and manipulate information in relational databases.
Applications commonly use it to authenticate users, process orders, retrieve customer records, manage inventory, and generate reports.
A vulnerability can appear when a developer combines SQL instructions and user-supplied values into a single query string without properly separating the two.
Consider a search feature that retrieves a customer record based on a name entered into a form.
If the application directly inserts that name into its SQL statement, specially crafted input may change how the database interprets the query.
The problem is not simply that an attacker entered unusual characters.
The underlying failure is that the application allowed input to influence the SQL instructions themselves.
SQL injection can affect applications written in different programming languages and connected to different database systems.
It can also appear in administrative tools, internal services, APIs, reporting functions, and background processes—not only public-facing website forms.
Why Is SQL Injection Dangerous?
The impact of SQL injection depends on the vulnerable query, the database configuration, the permissions assigned to the application's database account, and the information or operations exposed by the application.
Potential consequences include:
Unauthorized data access: Attackers may retrieve customer information, account records, confidential business data, or other database contents.
Authentication bypass: Vulnerable login queries may allow attackers to interfere with the application's authentication logic.
Data manipulation: An attacker may alter records, modify account details, or change business information if the affected database account permits those operations.
Data deletion: In some circumstances, vulnerable queries and excessive database permissions can expose records to destructive operations.
Business disruption: Compromised data, damaged records, and emergency remediation can interrupt services and undermine customer confidence.
Further compromise: Depending on the database engine, configuration, and privileges, a successful attack may create additional security risks beyond the original query.
These outcomes are possible consequences, not guaranteed results of every SQL injection vulnerability.
A read-only database account, for example, can substantially limit the damage an attacker might cause compared with an account that has broad administrative privileges.
SQL injection is therefore both a query-construction problem and a broader application security concern.
Preventing the vulnerability is essential, while limiting database permissions helps reduce the potential impact if another control fails.
1. Use Parameterized Queries and Prepared Statements
Parameterized queries are the most important starting point for preventing SQL injection.
A parameterized query separates the SQL statement's structure from the values supplied by users or other parts of the application.
Instead of assembling an executable query by inserting raw input into a string, the application defines the query and passes the values separately through the database API.
The database driver handles the parameter values according to the parameter-binding mechanism.
This prevents a value from being interpreted as additional SQL syntax within that parameterized statement.
For example, an application that searches for a customer should define the lookup condition in its SQL statement and bind the customer name as a parameter.
Even if the supplied name contains characters that resemble SQL instructions, those characters remain part of the value rather than changing the query's intended structure.
The same approach should be used for database operations that retrieve, insert, update, or delete records.
Parameterized queries are supported by database APIs across many programming languages.
The implementation differs between languages and drivers, but the security principle remains the same: SQL instructions and untrusted data must remain separate.
OWASP identifies prepared statements with variable binding as the primary defense because they help ensure that user input cannot change the intended meaning of a query.
Where developers commonly make mistakes
A query is not protected merely because the developer calls a prepared-statement API somewhere in the process.
The protection can be undermined if the application first concatenates untrusted input into the SQL text and then prepares the resulting statement.
In that situation, the malicious input may already have become part of the SQL instructions.
Another mistake is parameterizing one query while leaving other database operations vulnerable.
A secure login function does not make an application's search, filtering, reporting, or account-management functions automatically safe.
Developers should review every database query that uses dynamic values and confirm that those values are bound correctly.
2. Avoid Building SQL Queries Through String Concatenation
String concatenation becomes dangerous when an application combines SQL instructions with untrusted values to construct an executable statement.
This can happen when developers append input from website forms, URL parameters, API requests, cookies, imported files, or other sources directly to SQL strings.
A value does not need to come directly from a visitor to be untrusted.
Data received from another internal service or retrieved from a database may also require careful handling if its origin and integrity are not guaranteed.
The safer approach is to keep the query structure fixed wherever possible and pass changing values through parameter binding.
Code reviews should look for query construction that combines SQL keywords, operators, and user-controlled strings.
Particular attention should be given to older code, custom database wrappers, search functions, report builders, and code paths that were added after the application's original security review.
When dynamic SQL is genuinely necessary, developers should identify exactly which parts of the query need to change and use an appropriate safe construction method for each part.
The practical rule is to avoid concatenating untrusted data into executable SQL, even when the input appears harmless. Validation may reject inappropriate values, but it should not replace parameterized queries.
3. Validate Input Using Explicit Rules
Input validation is an important supporting control.
It helps an application determine whether a supplied value meets the requirements of the feature being used.
For example, a quantity field may accept only positive integers within an allowed range.
A date field may require a valid date.
A status field may accept only the statuses defined by the application.
These checks improve data quality and reduce the chance that unexpected values will enter application workflows.
However, input validation alone does not reliably prevent SQL injection.
Blocking a few suspicious characters or SQL keywords is insufficient because attack techniques can vary, and legitimate data may contain punctuation or other characters that simplistic filters reject.
OWASP recommends allow-list validation where appropriate.
Under this approach, an application defines the values, formats, or choices it accepts instead of relying exclusively on a list of forbidden characters.
Even then, accepted values should still be passed to SQL through parameterized queries.
Use allow-lists for query structure
One important limitation is that SQL parameters generally represent data values, not arbitrary parts of a query's structure.
For example, an application may allow users to sort a product list by price, name, or date.
A parameter placeholder cannot generally be used as a direct substitute for a column name or an SQL keyword such as ASC or DESC.
The application should therefore map the user's selection to a fixed, application-defined choice.
Unknown options should be rejected rather than appended to the SQL statement.
The same principle applies to dynamically selected table names, column names, and other structural elements.
Keep these choices under application control wherever possible, and use a narrowly defined allow-list when a feature genuinely requires selectable options.
Continue to parameterize the actual data values in the query.
This distinction matters because validation and parameter binding solve different problems: validation determines whether an input is acceptable, while parameter binding prevents a value from being interpreted as SQL syntax.
4. Use Object-Relational Mapping Tools Correctly
Object-relational mapping tools, commonly called ORMs, allow developers to work with database records through programming-language objects and framework APIs.
Depending on the framework and the operation, an ORM can generate SQL and handle parameter binding on the application's behalf.
This can reduce the need to assemble SQL statements manually.
However, using an ORM does not automatically make an application immune to SQL injection.
Developers can introduce vulnerabilities when they concatenate untrusted input into raw SQL expressions, use unsafe query-building features, or construct dynamic statements incorrectly.
An ORM may also provide both safe and unsafe ways to express a database operation.
Teams should understand how their selected ORM handles parameters and raw queries.
They should prefer documented, parameterized query interfaces and review any feature that accepts SQL fragments or dynamically constructed statements.
A useful review question is whether the framework treats the supplied value as data or incorporates it into the SQL instructions.
OWASP specifically warns that ORM queries can still be vulnerable when developers concatenate untrusted input rather than binding it as a parameter.
5. Implement Stored Procedures Safely
Stored procedures are database routines that applications can call to perform defined operations.
They can help centralize database logic and, when designed correctly, reduce the need for applications to construct complex SQL statements.
However, stored procedures are not automatically safe from SQL injection.
A procedure may still be vulnerable if it builds a dynamic SQL statement by concatenating untrusted input into the statement's text.
Passing a parameter safely into the procedure does not guarantee that the procedure handles that parameter safely internally.
Developers should prefer static SQL and parameterized operations inside stored procedures.
When dynamic SQL is necessary, the implementation should bind data values using the database engine's supported mechanism and handle structural choices separately.
Stored procedures should also be reviewed for excessive permissions and unintended access to database objects.
The relevant question is not simply whether the application uses stored procedures.
It is whether the complete operation—from the initial application call to the final database statement—keeps untrusted data separate from executable SQL.
6. Apply the Principle of Least Privilege to Database Accounts
The principle of least privilege means giving each account only the permissions it needs to perform its assigned tasks.
This control does not prevent SQL injection itself.
Instead, it limits the damage that may be possible if a vulnerability is exploited.
An application that only needs to retrieve product information should not connect to the database using an account with unrestricted administrative privileges.
Similarly, a component that only needs to read records should not automatically receive permission to modify or delete them.
Organizations should review database permissions and remove unnecessary privileges.
Where practical, they should use separate database accounts for applications or components with different responsibilities.
Teams may also consider database views or other access-control mechanisms that expose only the records or fields required for a particular function.
These mechanisms must be configured and tested correctly, and queries against them still need protection against SQL injection.
Administrative credentials should not be used as routine application credentials.
Access to database administration functions should be restricted to the accounts and workflows that genuinely require it.
OWASP recommends least privilege as an additional defense because reducing database permissions can constrain the potential impact of a successful injection attack.
7. Handle Database Errors Without Exposing Sensitive Information
Database errors are useful during development because they help developers diagnose problems with queries, connections, permissions, and data types.
Exposing detailed database errors to public users, however, can reveal implementation details that help an attacker understand the application.
Depending on the database and error, detailed messages may disclose table names, column names, query fragments, database technology, or other information about the application's internal structure.
Production applications should return appropriate, user-friendly error messages while recording the technical details needed for authorized troubleshooting in protected logs.
Error handling should not conceal failures from the development and security teams.
It should prevent unnecessary disclosure to users while preserving enough information for investigation.
Detailed errors should be accessible only to authorized personnel, and logs should be protected against unauthorized access.
Logging should also avoid unnecessarily recording passwords, authentication tokens, or other sensitive data.
Suppressing detailed error messages is a supporting safeguard, not a substitute for fixing the vulnerable query.
An application may remain vulnerable even when it does not display a database error.
8. Keep Database Software, Drivers, and Frameworks Updated
Applications depend on database engines, database drivers, programming-language libraries, frameworks, and other components.
Security weaknesses or outdated implementations in these dependencies can create additional risks.
Organizations should track the components their applications use, monitor relevant security advisories, and apply supported security updates according to their risk and maintenance requirements.
Updates do not replace safe query construction.
A fully patched database can still execute an unsafe query supplied by a vulnerable application.
Likewise, upgrading a framework does not guarantee that custom query-building logic is safe.
Developers must review how the application uses the updated component, particularly where raw SQL or dynamic statements are involved.
A sound maintenance process combines dependency management, security updates, code review, and testing.
Teams should verify that updates have been applied successfully and that important application functions continue to work as expected.
9. Test Applications for SQL Injection Vulnerabilities
Security testing helps organizations identify unsafe query construction before attackers exploit it.
Testing should be included throughout the software development lifecycle rather than treated as a one-time activity before launch.
New features, database changes, framework upgrades, and changes to authentication or search functions can introduce new risks.
A practical testing program includes the following activities:
Code review: Examine database queries, stored procedures, ORM usage, and dynamic SQL construction.
Confirm that untrusted values are parameterized and that dynamic identifiers come from controlled choices.
Automated security testing: Use suitable static analysis and dynamic application security testing tools to identify potentially unsafe query construction and observable injection behavior.
Automated tools can help prioritize investigation, but their findings require appropriate review.
Manual security testing: Have qualified testers assess database-related functionality that automated tools may not fully understand.
Testing should be authorized and conducted within a defined scope.
Regression testing: After a vulnerability is fixed, add tests where practical to help prevent the same weakness from returning in future releases.
Verification of remediation: Confirm that the corrected application uses safe query construction and that the original vulnerability can no longer be reproduced under the relevant test conditions.
OWASP's SQL Injection Prevention Cheat Sheet and Web Security Testing Guide provide established reference material for prevention and security testing.
Test only systems you are authorized to assess
Security testing should be performed on systems the organization owns or has explicit permission to test.
Production testing requires appropriate authorization, safeguards, and coordination to avoid disrupting real users or damaging data.
Where possible, developers should use controlled test environments with representative configurations and non-sensitive test data.
10. Use a Web Application Firewall as an Additional Layer
A web application firewall, or WAF, can inspect HTTP traffic and block requests that match configured security rules.
Depending on the product and configuration, a WAF may help detect or mitigate some SQL injection attempts.
However, a WAF should not be treated as the primary solution to unsafe database queries.
Traffic inspection can miss attacks, produce false positives, or fail to understand the application's intended behavior.
It may also be unable to protect vulnerable database operations that occur through channels outside the traffic it inspects.
Organizations should use a WAF as part of a broader security architecture, alongside parameterized queries, secure application design, least-privilege database accounts, monitoring, and regular testing.
WAF rules should be configured, maintained, and evaluated against the application's actual requirements.
Teams should investigate alerts and verify that protective rules work as intended rather than assuming that deploying a WAF makes vulnerable code safe.
The objective is defense in depth: multiple controls that address different parts of the risk, with secure query construction remaining the essential application-level defense.
A Practical SQL Injection Prevention Checklist
Before releasing an application or making a significant database-related change, developers and security teams should confirm that the following controls are in place:
Database queries use parameterized statements for untrusted data values.
Application code does not concatenate untrusted input into executable SQL.
Input validation follows explicit business rules and allow-lists where appropriate.
Dynamic table names, column names, sort directions, and other query-structure choices are controlled by the application.
ORM features and raw SQL interfaces are reviewed for unsafe query construction.
Stored procedures do not create vulnerable dynamic SQL internally.
Database accounts have only the permissions required for their responsibilities.
Administrative credentials are not used as routine application credentials.
Public error messages do not expose unnecessary database details.
Database engines, drivers, frameworks, and dependencies receive appropriate security updates.
Automated and manual security tests cover relevant database operations.
Fixes are verified, and regression tests are added where practical.
Monitoring and incident-response procedures are available to investigate suspected exploitation.
The checklist should be applied to the entire application, not only the login page.
Search, reporting, account management, filtering, sorting, and administrative functions can all interact with databases and deserve appropriate review.
Final Verdict: Prevent SQL Injection at the Query Level
Preventing SQL injection starts with a clear engineering rule: never allow untrusted input to change the structure of an executable SQL statement.
Parameterized queries and prepared statements provide the primary defense.
Input validation, carefully implemented ORMs and stored procedures, least-privilege database accounts, secure error handling, dependency updates, security testing, and WAF protection provide additional safeguards.
For development teams, the most effective approach is to make safe database access the default in application architecture, code reviews, and development standards.
For organizations maintaining existing software, reviewing dynamic queries and removing unsafe string concatenation are practical priorities.
No single control guarantees that an application is secure.
A consistent combination of secure coding, restricted permissions, testing, and maintenance provides a stronger foundation for protecting databases and the people whose information they contain.